The Core Verification Framework: Five Signals to Check Together
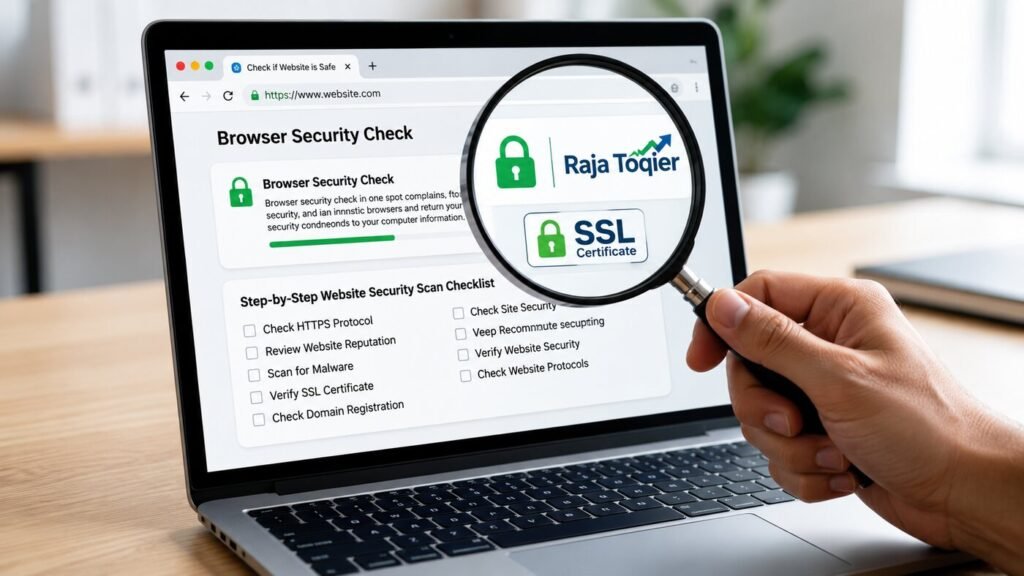
In order to make sure a website is safe to browse, check for five key indicators simultaneously: secure HTTPS encryption, Google Safe Browsing score, no blacklisting, proven domain age and contact information for the corporation. Just like the reputable seo technology service uses only objective technical indicators rather than assumptions, safe browsing should be based on verifiable facts, not initial impressions.
None of these signals is enough on its own. A website may have a padlock symbol, yet be running a phishing kit under it. A site can be years old and still get compromised overnight. The framework below treats website safety the way a security engineer would: as a stack of independent checks, each catching a different failure mode.
In case you need a thorough, hands-off analysis of any of the points listed above, you can leverage our professional website security audits to cover all vulnerability layers automatically.
Top Automated Scanner Engines for Instant URL Vetting
The quickest way to check if a website is safe is to run a multi-engine scan on its URL even before opening it in a web browser. Every one of the engines provided here uses a different detection method; thus, using several engines at once will provide a much better view than just one.
| Scanner | Update Frequency | Detection Method | Main Limitation |
| Google Safe Browsing | Continuous, real-time | Blacklist Database Cross-Referencing across billions of URLs | Only flags sites already reported or crawled |
| Sucuri SiteCheck | Daily crawl cycles | Malware Signature Matching and Defacement Monitoring | Limited visibility into server-side scripts |
| URLVoid | Aggregated, near real-time | Combines dozens of third-party blocklists into one score | Depends entirely on partner engine accuracy |
The following tools use signature matching, which means detecting known malicious code, and not blocklist aggregators, which detect known malicious reputation. A brand-new malicious domain can slip past both for a short window, which is why manual heuristics still matter.
You will be able to verify if the link is suspicious or safe via the Google Transparency Report, which checks whether Google considers the domain to be harmful.
Deciphering the On-Page Infrastructure: Crucial Manual Security Indicators
Automated scanners catch known threats. Manual review catches the newer ones. Follow these steps each time you come across a new website:
- Check if the domain uses HTTPS and not just the HTTP protocol.
- Look for a privacy policy page and corporate address or registration of the company.
- Examine the copywriting for any grammar inconsistencies and urgency-based messages.
- Hover over navigation links to preview where they actually resolve.
- Look up the domain’s registration history before entering any payment details.
Beyond the Lock Icon: Auditing SSL/TLS Handshakes and Endpoint Security Protocols
A padlock in the address bar guarantees that there is an SSL/TLS Encryption connection between your browser and the server. It says nothing about what that server does with your data. The distinction that actually matters is which cryptographic protocol is running underneath.
- TLS 1.0 and 1.1: obsolete protocols, subject to known downgrading attacks and considered obsolete by modern web browsers.
- TLS 1.2: still a popular protocol that is okay to use, although getting older.
- TLS 1.3 (Endpoint Security Protocol): the latest version with improved speed of handshaking and stronger forward secrecy.
To find out the version of the handshake protocol, click on the padlock and then on the connection details page, where the version along with other important information is displayed.
Contextual Quality Signs: Catching Typosquatting and Server-Side Redirect Traps
Two related but distinct tricks are at play here. Typosquatting registers common misspellings of a legitimate domain, while homograph (or homoglyph) attacks swap in look-alike characters, such as an uppercase ‘I’ for a lowercase ‘l’, or add a stray dash so the fake domain reads as almost identical to the real one.
Even more worrying are the server-side redirect traps wherein the domain name looks legitimate, yet a server-side script redirects the user through multiple redirections before reaching the phishing web page. The good thing about such attacks is that the browser will hardly ever display any warnings since the starting domain is legitimate.
To learn more about finding malicious scripts, see our comprehensive breakdown on cleaning hidden website malware, which explains in detail how these redirect chains get implanted and removed.
Not sure if your own site passes these checks?
Our team runs a full technical audit covering SSL configuration, blacklist status, and hidden redirect scripts.
Deep System Architecture: Bridging the Semantic Gaps in Competitor Content
Most guides end there with scans and an SSL check only. Real digital safety is built deeper, in the infrastructure layer that most visitors never see. If you’re evaluating a website you manage yourself, these four areas separate a genuinely hardened domain from one that just looks safe on the surface.
Elite DNS Security Protocols: CAA Records, DNSSEC, and DMARC Realities
Domain trust starts before a browser even loads a page, at the DNS routing level. Three protocols do most of the work:
- CAA records indicate which certificate authorities are permitted to issue SSL certificates for a particular domain, disallowing malicious certificate issuance.
- DNSSEC (Domain Name System Security Extensions): cryptographically signs DNS responses so they can’t be silently rerouted by an attacker.
- SPF, DKIM, and DMARC alignment confirms that the emails are truly sent from the claimed domain and not a spoofed phishing email sent “from” the brand’s domain name.
Content Security Policy (CSP) Headers and Cross-Origin Resource Isolation
The Content Security Policy headers give instructions to the browser about which sources are permitted to include scripts, styles, and frames in the page. Without a correctly configured CSP policy, an injected script could run completely unchecked.
- Content Security Policy headers dictate the list of domains that can deliver executable scripts.
- CORS (Cross-Origin Resource Sharing) determines which foreign domains are permitted to make requests to the server.
- X-Frame-Options header helps prevent clickjacking attacks by ensuring that the page cannot be loaded within a hidden iframe on another site.
Properly configured headers stop cross-site scripting (XSS) attacks structurally, before any malware signature ever gets generated.
Server-Side Tracking Integrity & First-Party Data Privacy Isolation
With the decline in the use of third-party cookies, analytics have been migrated to server-side tag management systems. This raises a different challenge, where if server-to-server webhook validation is not used, personally identifiable data will leak from browser network logs to third-party endpoints in ways that are completely imperceptible in cookie audits.
Eliminating Subdomain Hijacking and Abandoned Digital Asset Vulnerabilities
An orphaned subdomain, one still pointing to a decommissioned cloud bucket or a canceled SaaS account, is one of the easiest ways for an attacker to take over a trusted-looking address. The reclamation workflow:
- Create a full export of all the DNS entries on the domain name.
- Check each subdomain for the existence of any live domain.
- Delete or update any DNS record that points to any abandoned cloud endpoint.
- Re-audit quarterly, since new subdomains get created faster than most teams track them.
For a full walkthrough of every layer covered so far, see our ultimate website security check guide to protect your site from cyber threats, or explore our technical SEO audit services if search visibility and technical health need to be reviewed together.
The Role of Temporal Data: Domain Age Verification and Risk Calculation
A simple WHOIS lookup tells you when a domain was registered. New risk modeling frameworks give even more importance to any kind of changes in registration details, such as recent changes of registration or sudden changes in nameservers. Even though a ten-year-old domain name may carry less risk, if there is a recent change of registrar, then more attention must be paid.
Compliance & Risk Mitigation Frameworks: The Institutional Trust Standards
In evaluating vendors, partners, and acquisitions, safety assessments become much more formalized compliance assessments.
| Framework | What It Covers | Digital Safety Signal |
| ISO/IEC 42001 Compliance | Responsible AI management systems | Governance maturity for AI-driven infrastructure |
| KYB (Know Your Business) Automation | Verified business identity and ownership | Reduces shell-company and fraud risk |
| Anti-Money Laundering (AML) Compliance | Financial transaction screening | Confirms legitimate operational funding |
These frameworks matter most for B2B due diligence, where the question isn’t just ‘is this page safe to click’ but ‘is this a real, accountable organization.’
Managing security and compliance for a growing site?
From CSP header configuration to DNSSEC rollout, our engineers handle the infrastructure layer end to end.
Traditional SEO Indicators vs. Next-Generation GEO Benchmarks
Search behavior itself is shifting from manual review toward AI-assisted verification. Generative Engine Optimization (GEO) reflects a parallel set of trust signals that AI answer engines now weigh alongside classic SEO factors.
| Signal | Traditional SEO View | GEO / AI Overview View |
| Page Speed | Ranking factor | Secondary; structural trust weighted higher |
| Content Structuring & Schema Markup | Helps rich snippets | Directly determines AI citation eligibility |
| HTTPS | Binary ranking signal | One input among many transit-security checks |
| Domain Age | Minor trust factor | Weighted against ownership-change volatility |
| Backlinks | Primary authority signal | Supplemented by structured entity clustering |
Want your content structured for AI citation, not just search rankings?
See how our team blends technical security hardening with modern GEO content architecture.Visit rajatoqier.com
Website safety requires more than a single evaluation checklist; it requires a posture that involves results of scanner analyses, manual heuristics, and technical hardening. If you’d rather have a specialist walk through your specific domain, ownership history, and header configuration with you directly, book a consultation and we’ll map out exactly where your site stands.
Frequently Asked Questions
Yes. HTTPS only ensures that data transferred between your browser and the server is safe. HTTPS cannot give any guarantees regarding the server’s intentions, hygiene, or ownership. Scammers use phishing pages with legitimate SSL certificates but also use Server-Side Redirect Traps and credential harvesting scripts.
Second-generation AI bots assess the domains via structured data analysis as opposed to surface-level judgment. That includes Generative Engine Optimization (GEO) markup, verifiable security infrastructure like DNSSEC and CSP headers, and, for business entities, a clean KYB automation history. Sites that have entity identification characteristics as well as a good technical hygiene score are higher than sites that depend on their backlinks alone.
Feed the URL to an engine like Malware Signature Matching, coupled with real-time blocklists such as the Google Safe Browsing report, along with Sucuri SiteCheck or URLVoid. For ongoing protection rather than a one-time check, a professional website security ecosystem monitors continuously instead of scanning a single moment in time.
A legitimate site has an HTTPS certificate on at least TLS 1.2, a privacy policy, business contact information, no blacklisted warnings on any of the scanners, as well as DNS records that have CAA and DNSSEC settings. Consistent professional copy without urgency-related pop-ups serves as supporting evidence.
If there is a ‘Not Secure’ warning in the website’s address bar, it indicates that the page is not encrypted using the HTTPS protocol and, hence, all data will be transmitted without encryption. Thus, any website that displays such a warning should not be trusted at all.